
ON DEMAND · ASSOCIATION OF LEGAL ADMINS HYBRID EVENT
The Hidden Cyber Risks in Everyday Law Firm Operations
Moving from "we have a process" to knowing how it actually works.
Most established law firms already have cybersecurity policies, backups, access controls, and vendor procedures.
But years of growth, staff changes, exceptions, and new technology can create gaps between what your firm
believes is happening and what actually happens day to day. This session walked through where those gaps tend to hide.
Watch the Session
Recorded live on Thursday, October 8th, 2026. 45 Minutes | Presented by Graham Roggli, Client Strategy Manager at Xantrion
Graham walks legal administrators through five situations most firms run into, and the questions worth asking about each.
Your Firm Has Security Processes.
But Do They Still Work?
Having a cybersecurity policy is one thing. Knowing that it’s consistently followed, and being able to prove it, is another.
Over time, even well-run law firms accumulate exceptions: permissions that no longer match someone’s role, temporary workarounds that become permanent, technology adopted outside normal processes, or recovery plans that haven’t been tested against how the firm operates today.
Graham unpacked those everyday operational gaps and the business risks they can create.
What the Session Covered
- Access: Do the right people have access—and can you explain why?
- Exceptions: Where have temporary workarounds become the norm?
- AI & Technology: Can your firm innovate without losing control of its information?
- Compliance: Can you prove the security claims you make to clients and insurers?
- Resilience: What happens when critical technology is unavailable longer than expected?
What You'll Take Away
How to spot gaps between what’s defined, consistently performed, and actually demonstrable—and the questions you should be asking your leadership, internal teams, and technology partners.
Start With a Cybersecurity Risk Assessment
Knowing the questions is the easy part. Answering them about your own firm means sitting down with the people who can tell you what actually happens, not what’s supposed to. The Cybersecurity Risk Assessment Guide gives you that review in a form you can take to your leadership, your internal team, or whoever handles your IT, so you come back with answers instead of impressions.
Meet your Speaker
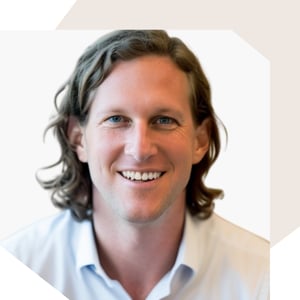
GRAHAM ROGGLI
CLIENT STRATEGY MANAGER, XANTRION
Graham led this 60-minute session using realistic situations legal administrators routinely encounter to connect cybersecurity decisions with the outcomes that matter to the business: client trust, productivity, leadership confidence, financial exposure, and the ability to keep the firm operating when something goes wrong.
Give Your Firm the Same Checkup
Graham’s five situations all come back to three questions: what should happen, who’s responsible, and how do you know it happened.
If you want to put your own firm through that review, this is where to start.